


Connect risks and measures
Asset and supplier information supports prioritisation.
Suggestions appear from three characters.
No match. Try another term or choose a topic below.
Validate the controller against a model
The topic area at a glance
Customers we work for
Joint projects and their results
Working at IQstruct Engineering
ISO 9001 and TISAX
Alliances, associations, marketplaces
Quality policy and certificate
Organise responsibilities, risks and evidence in an operable information security management system.
Documents alone are not enough if responsibilities and measures remain unclear in everyday work. Companies need a traceable link between requirements, implementation and evidence.
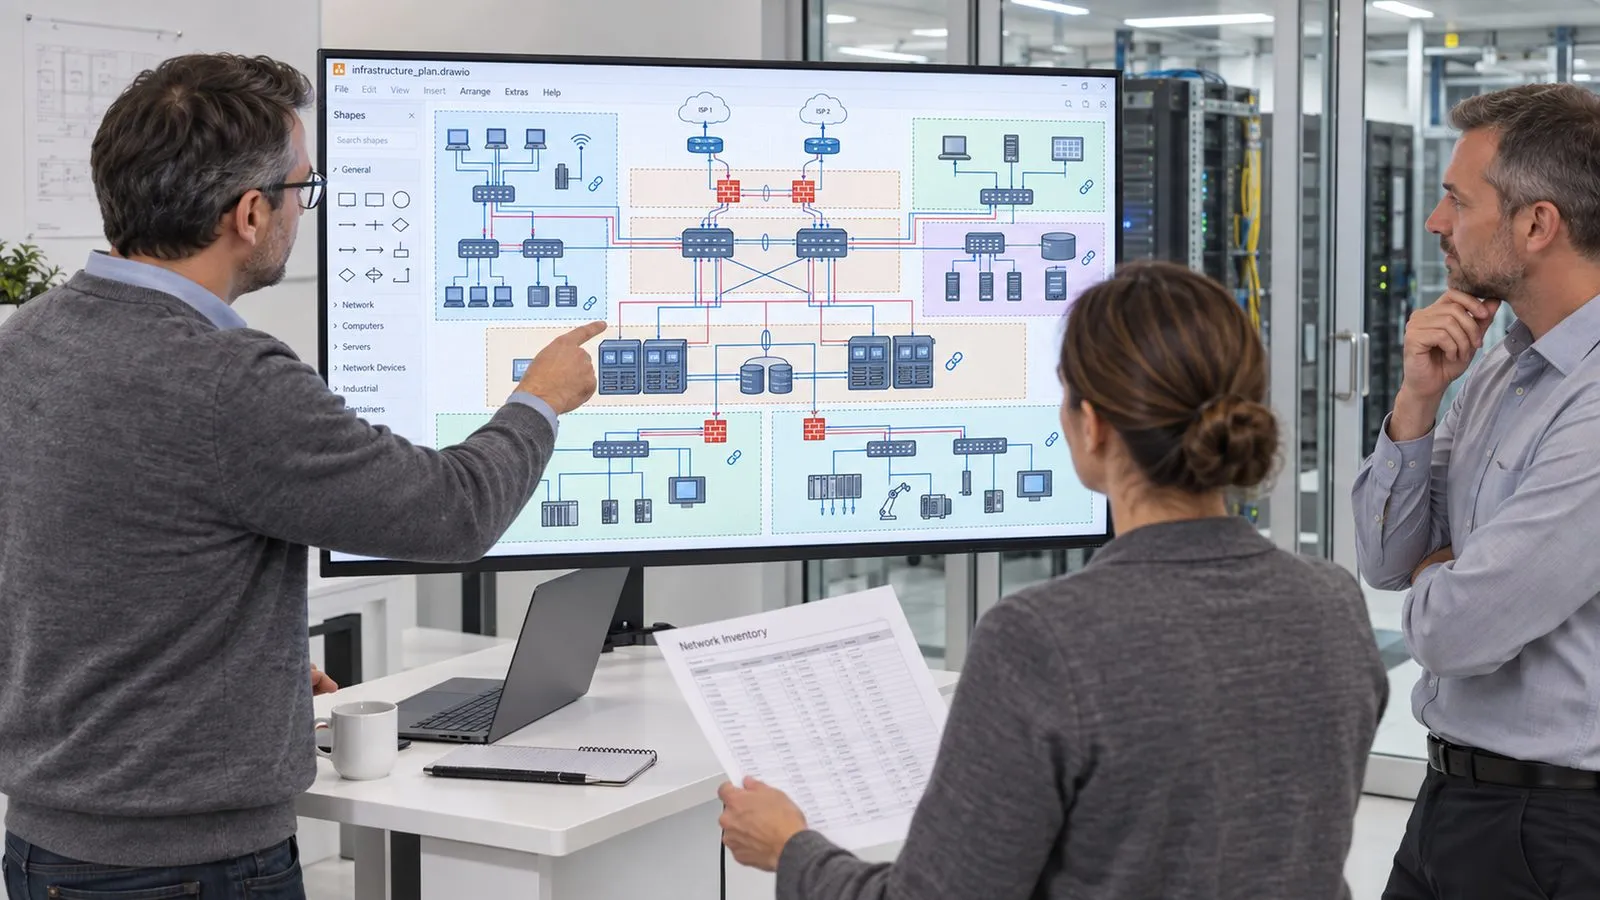
IQstruct Engineering supports internal audits, supplier audits and the technical and organisational preparation of external assessments. The offer includes tracking of measures, document maintenance and external roles as ISMS team, IT security officer or quality management officer. Requirements are considered together with the existing system landscape.
In a free first conversation we place which rule sets apply to you and which records are already in hand.
Asset and supplier information supports prioritisation.
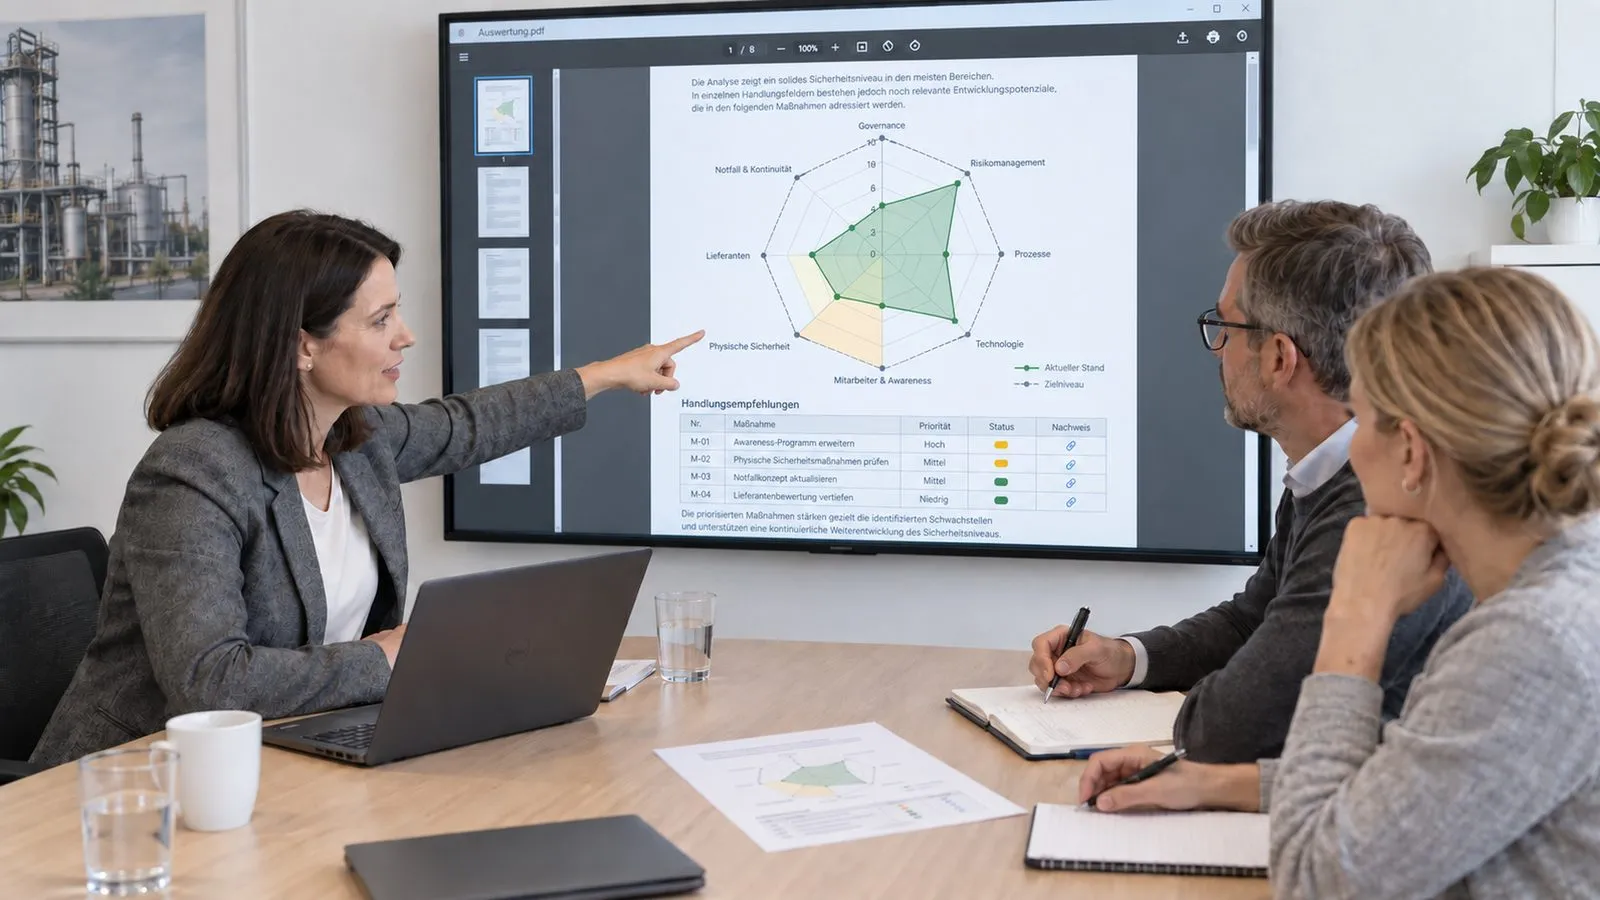
Audit report, findings, action plan and evidence overview are prepared to suit the order.
External officer roles can support the ongoing work.
IQstruct Engineering supports internal audits, supplier audits and the technical and organisational preparation of external assessments.
We accompany TISAX, ISO 27001, NIS2, the Cyber Resilience Act, the EU AI Act, the EU Data Act as well as requirements from the ecodesign regulation and for the digital product passport. We review documents, classify requirements technically and organisationally and give implementation guidance; open legal questions are clarified by qualified legal advisers. For plants and automation systems, we additionally offer the provision of evidence under IEC 62443.
Tracking of measures, document maintenance and internal audits remain relevant after an audit as well. For this, IQstruct Engineering provides lasting support as an external ISMS team or as IT security or quality management officer, coordinated with your existing responsibilities.
Information security
Responsibilities, risks and evidence are organised in an operable information security management system.
 Ai
1
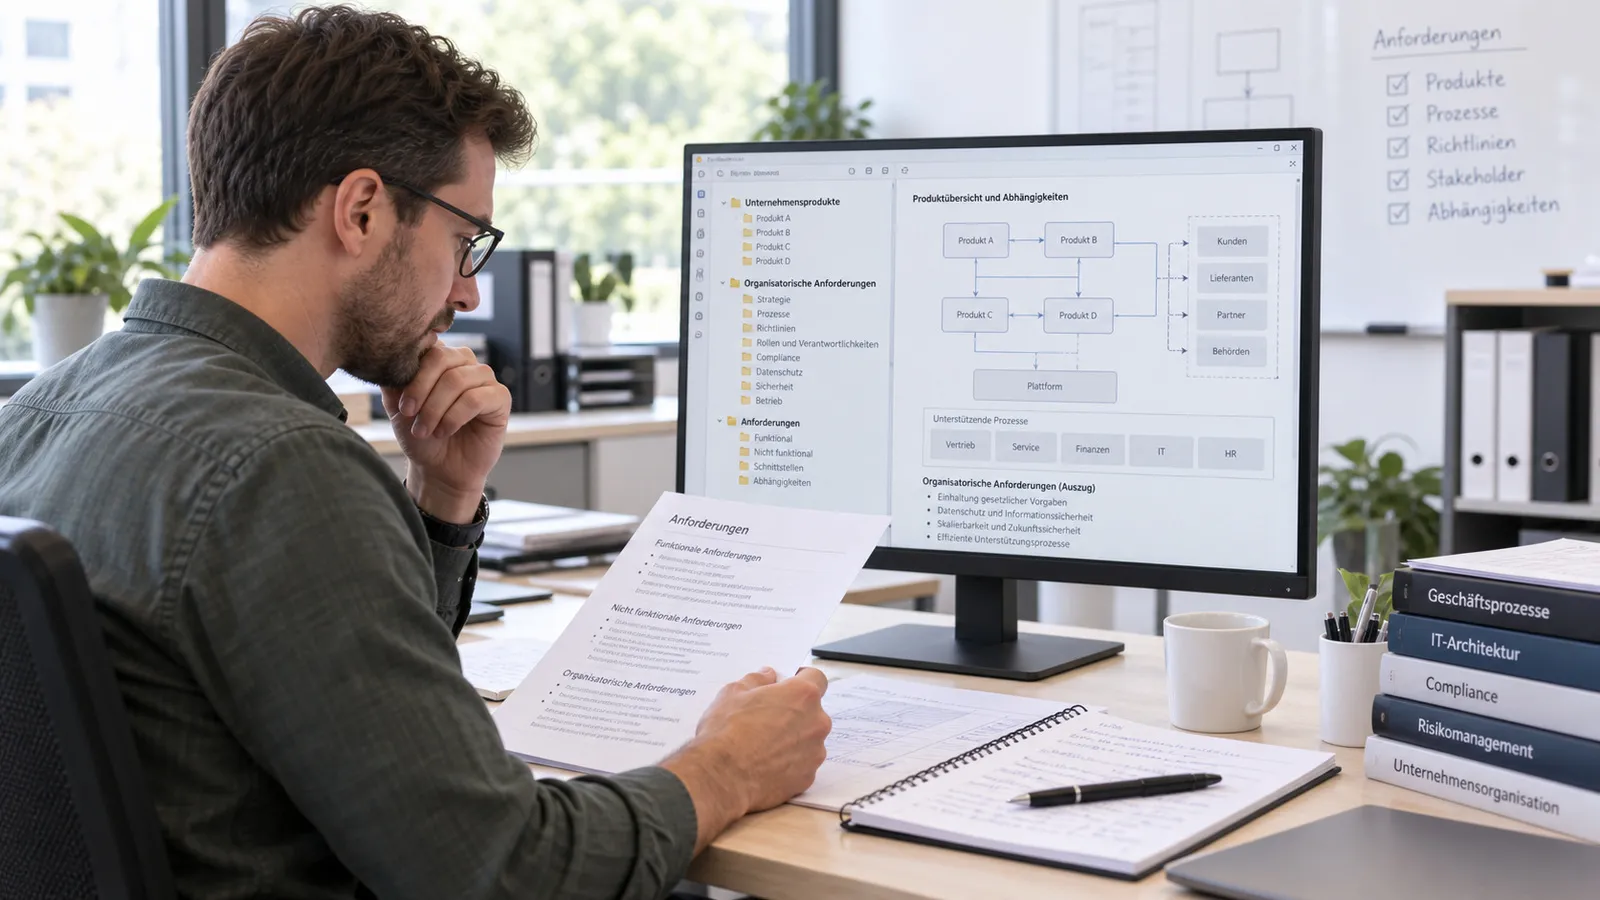
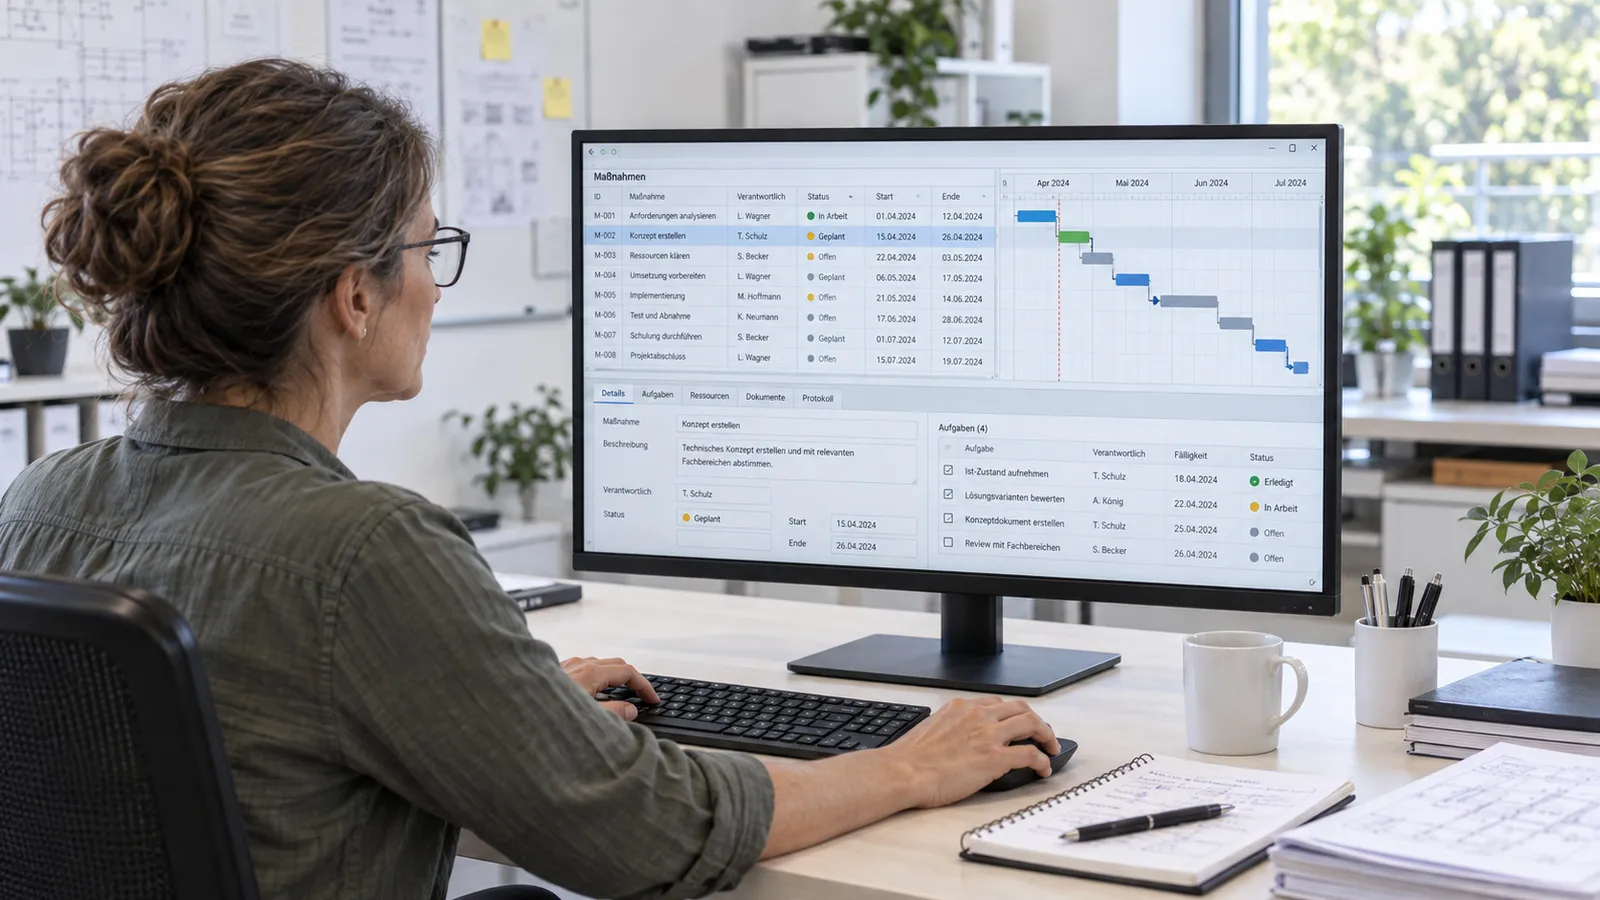
Determine requirements
The company's products and organisational requirements are reviewed.
 Ai
2
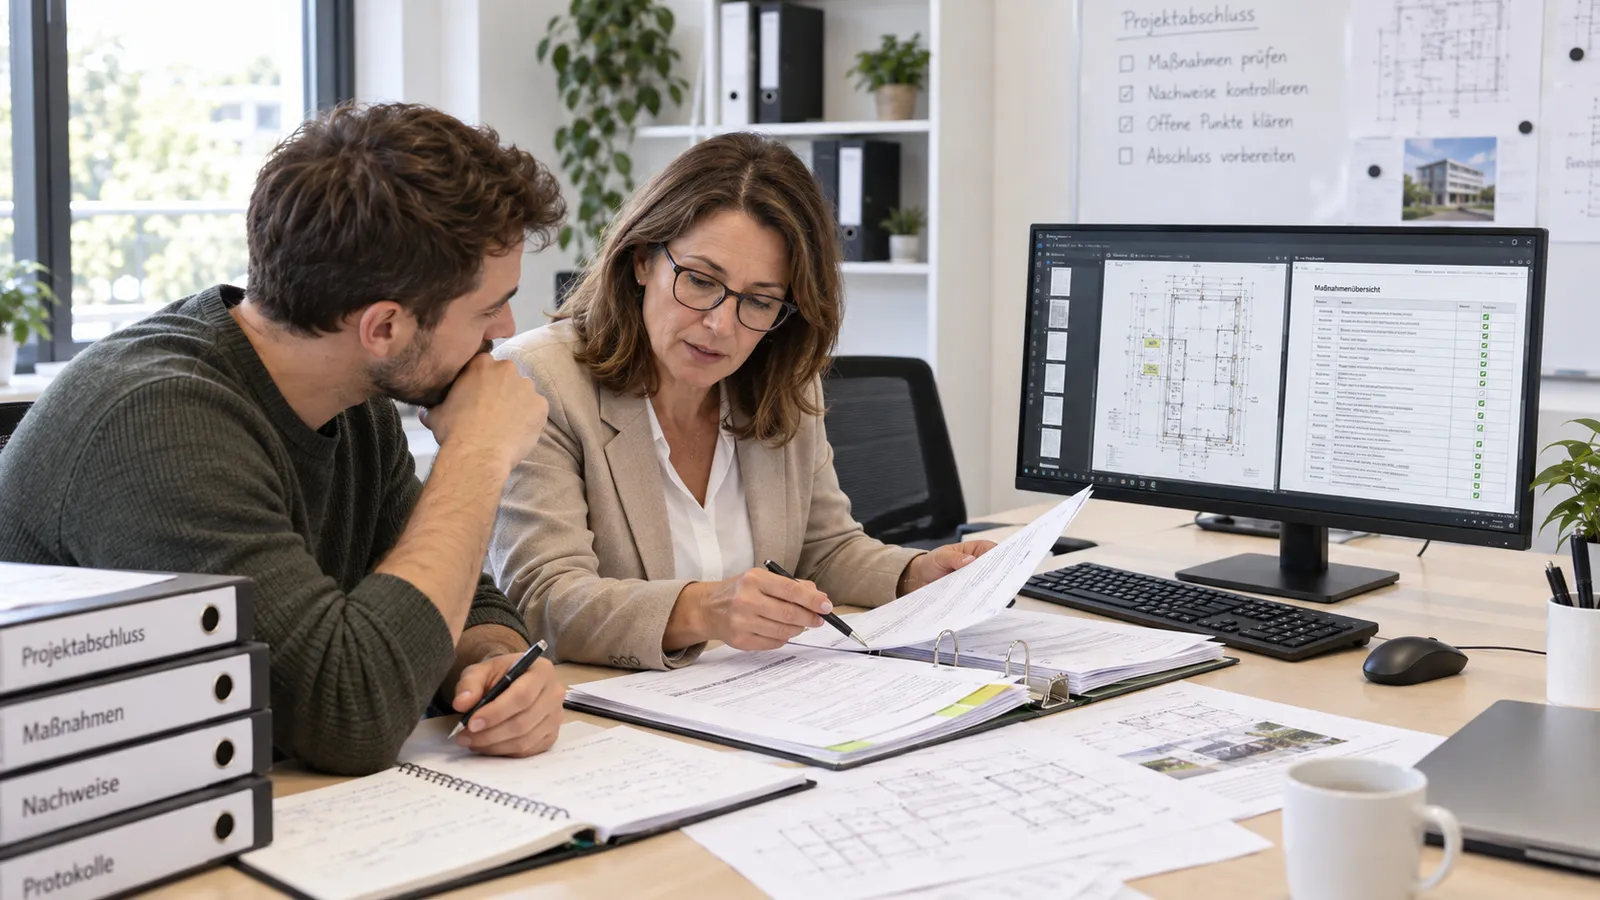
Plan measures
Responsibilities, tasks and dates are set out in an overview of measures.
 Ai
3
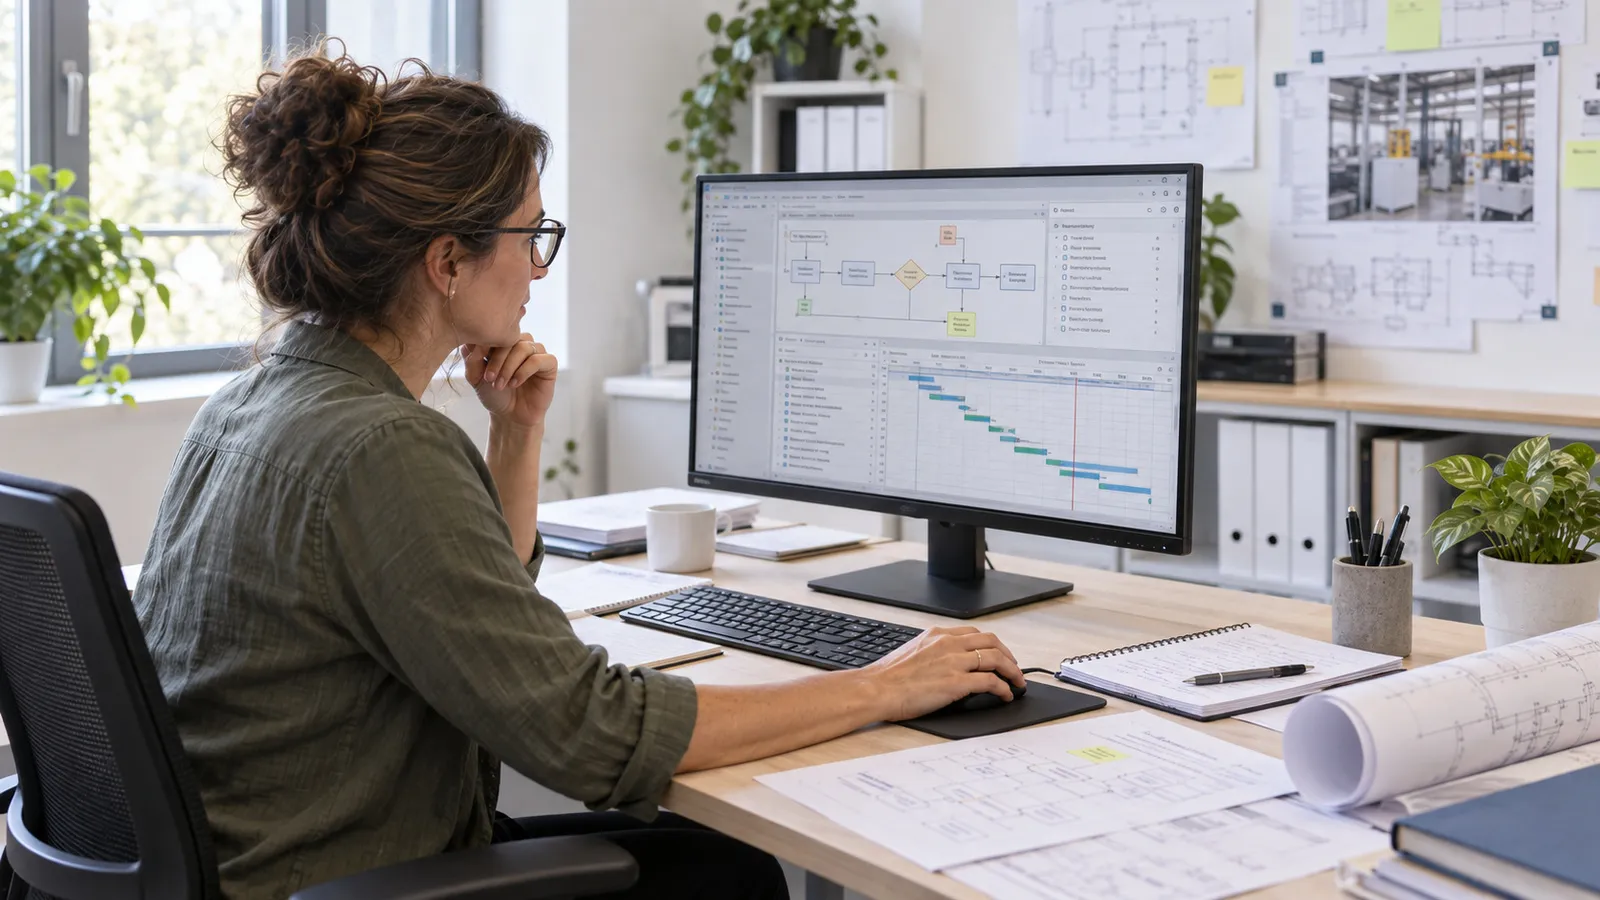
Prove implementation
Internal measures and project completion are checked against the documents.
 Ai
4
Accompany changes
New requirements are incorporated into the action plan and the company's processes.
The CyberRisikoCheck based on DIN SPEC 27076 offers a structured start to the survey of IT security.
Internal audits show where measures and evidence are still missing.
IQstruct Engineering takes on the role of ISMS or IT security officer.
Information security
In the automotive industry, TISAX creates a common basis for handling confidential information.
Manufacturers and suppliers exchange design data, software and further sensitive project information. TISAX makes it possible to assess information security against common criteria and to share the results with business partners. As an engineering service provider in this supply chain, IQstruct Engineering likewise commits to protecting the information entrusted to it and holds a TISAX label. Clear access rights, governed data exchange and traceable responsibilities are therefore part of the cooperation in a project as well.
We are glad to answer your detailed questions in a personal conversation.
The final assessment is made by the responsible independent certification body. We prepare documents and evidence structures for it.
IQstruct Engineering classifies requirements technically and organisationally. Binding legal assessments are made by external experts.
Audit report, documented findings, risk assessment, prioritised action plan and evidence overview.
Every industry has its particularities. That calls for a reliable partner who knows the requirements and delivers suitable solutions.
First conversation
Describe your task. We agree a date and discuss the possible project scope.
 Ai
1
You request an appointment
 Ai
2
We discuss your requirements
 Ai
3
You receive a quotation for the agreed scope
Describe your task in the contact form. We come back with a proposed date.
Arrange a first conversationBooking calendar
The booking calendar appears here. It loads only after your consent, because your browser connects to Microsoft in the process.
Discover further suitable services.
Make components, licence terms and updates traceable.
Classify requirements technically and organisationally before individual tools turn into operational processes.
Combine monitoring, updates and support in one agreed operating model.
