


Record components transparently
Product components and versions form the basis for further assessment.
Suggestions appear from three characters.
No match. Try another term or choose a topic below.
Validate the controller against a model
The topic area at a glance
Customers we work for
Joint projects and their results
Working at IQstruct Engineering
ISO 9001 and TISAX
Alliances, associations, marketplaces
Quality policy and certificate
Make components, licence terms and updates traceable.
Dependencies and forms of provision influence which evidence and measures a software product requires. Without an overview, assessing new vulnerabilities and licence obligations becomes laborious.
IQstruct Engineering supports the technical and organisational preparation of product requirements. Open source components are examined with regard to planned use, modification and distribution. An SBOM can complement the component overview. Manufacturer notices and updates are integrated into test and operating processes.
In a free first conversation we sort out which of your products fall under the regulation and which records are still missing for them.
Product components and versions form the basis for further assessment.
Relevant conditions are agreed with the customer.
Testing, maintenance windows and rollback connect development and later operation.
IQstruct Engineering supports the technical and organisational preparation of product requirements, including those from the Cyber Resilience Act.
Before an open source component is used, we check the licence type, commercial use, modification, distribution and server-side provision. Copyleft licences such as the AGPL are distinguished from permissive licences such as MIT; relevant conditions are documented and agreed with you.
An SBOM complements the component overview and supports later vulnerability and update processes. Manufacturer notices and security updates are monitored and brought into operation via relevance, testing, release, rollout and rollback.
Product compliance
A traceable component overview makes it easier to assess new vulnerabilities and licence obligations.
 Ai
1
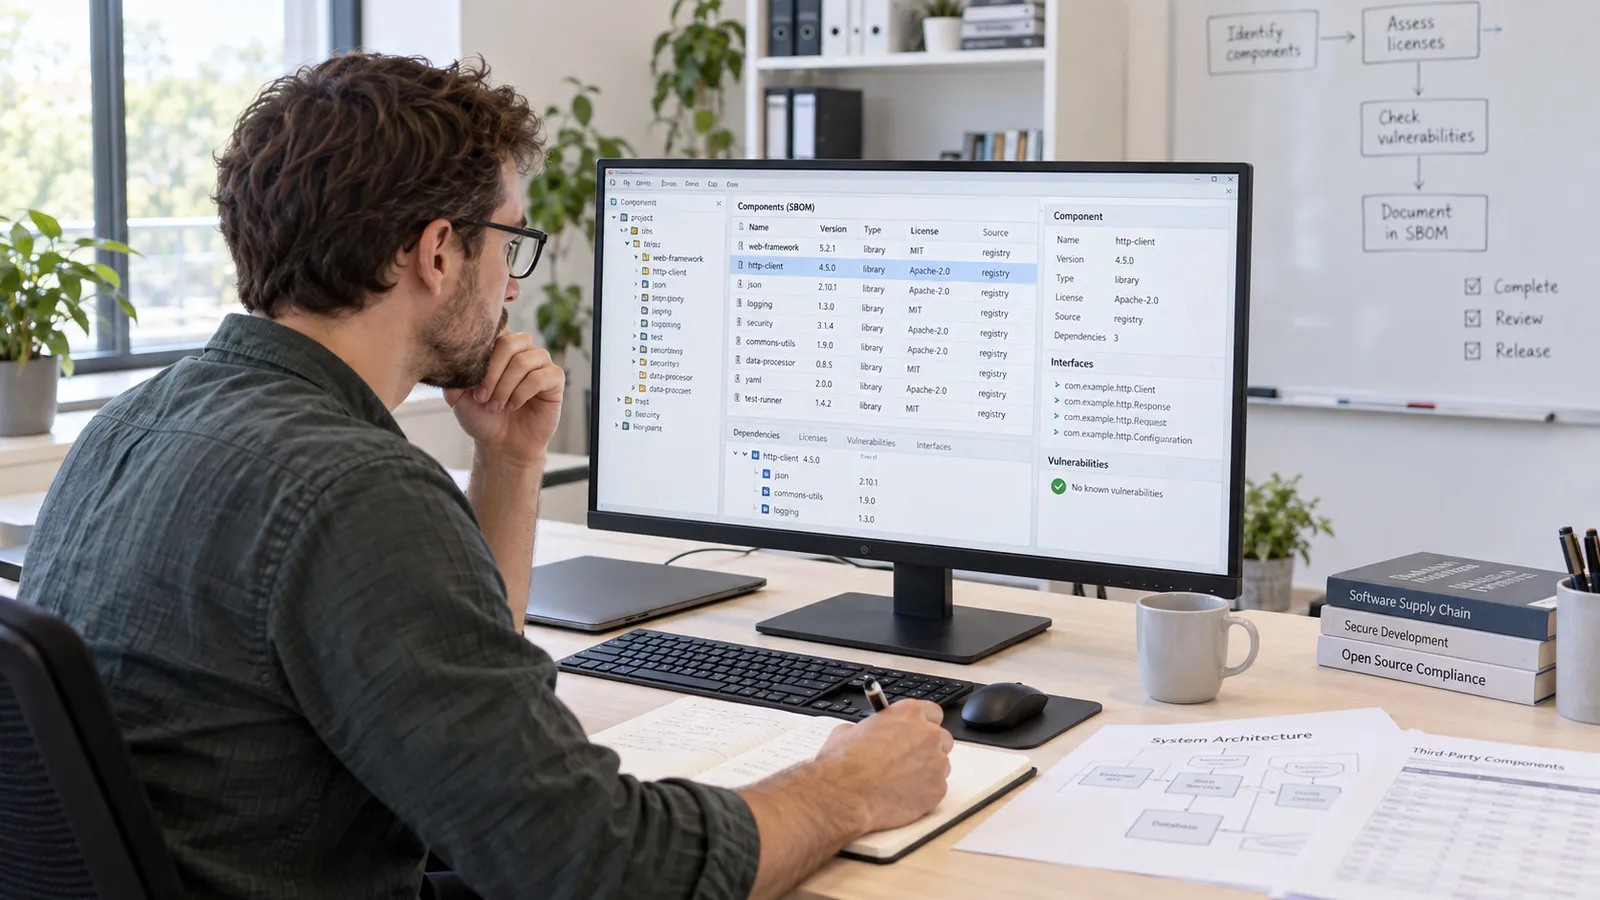
Record digital products
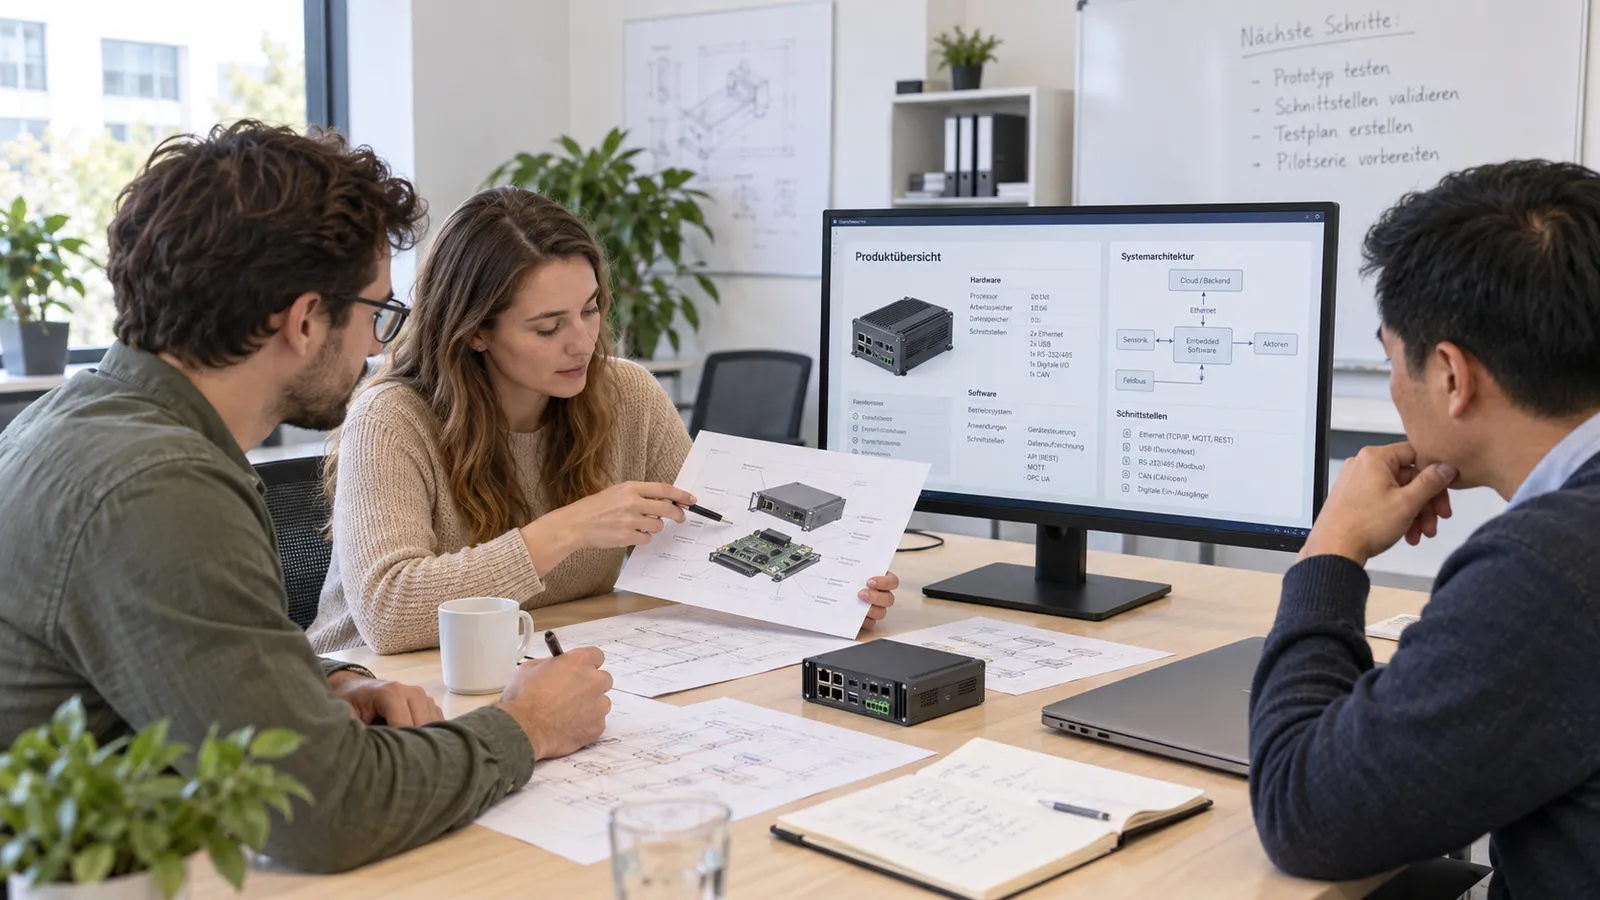
Products with embedded software and their interfaces are recorded.
 Ai
2
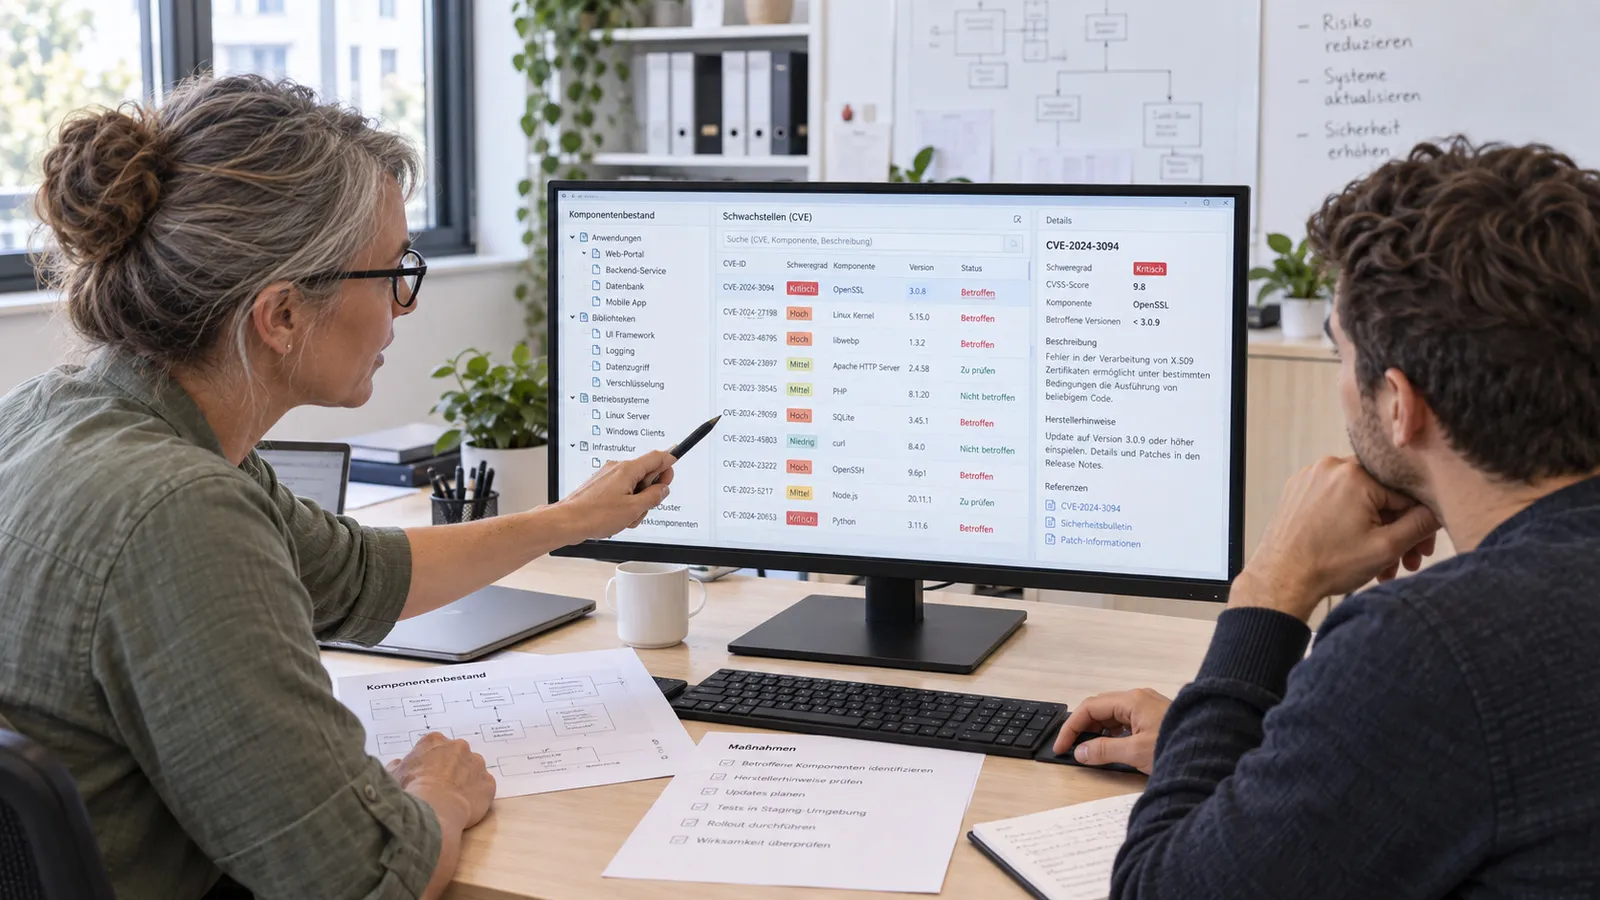
Assess components
Software components, libraries and licences are listed in an SBOM.
 Ai
3
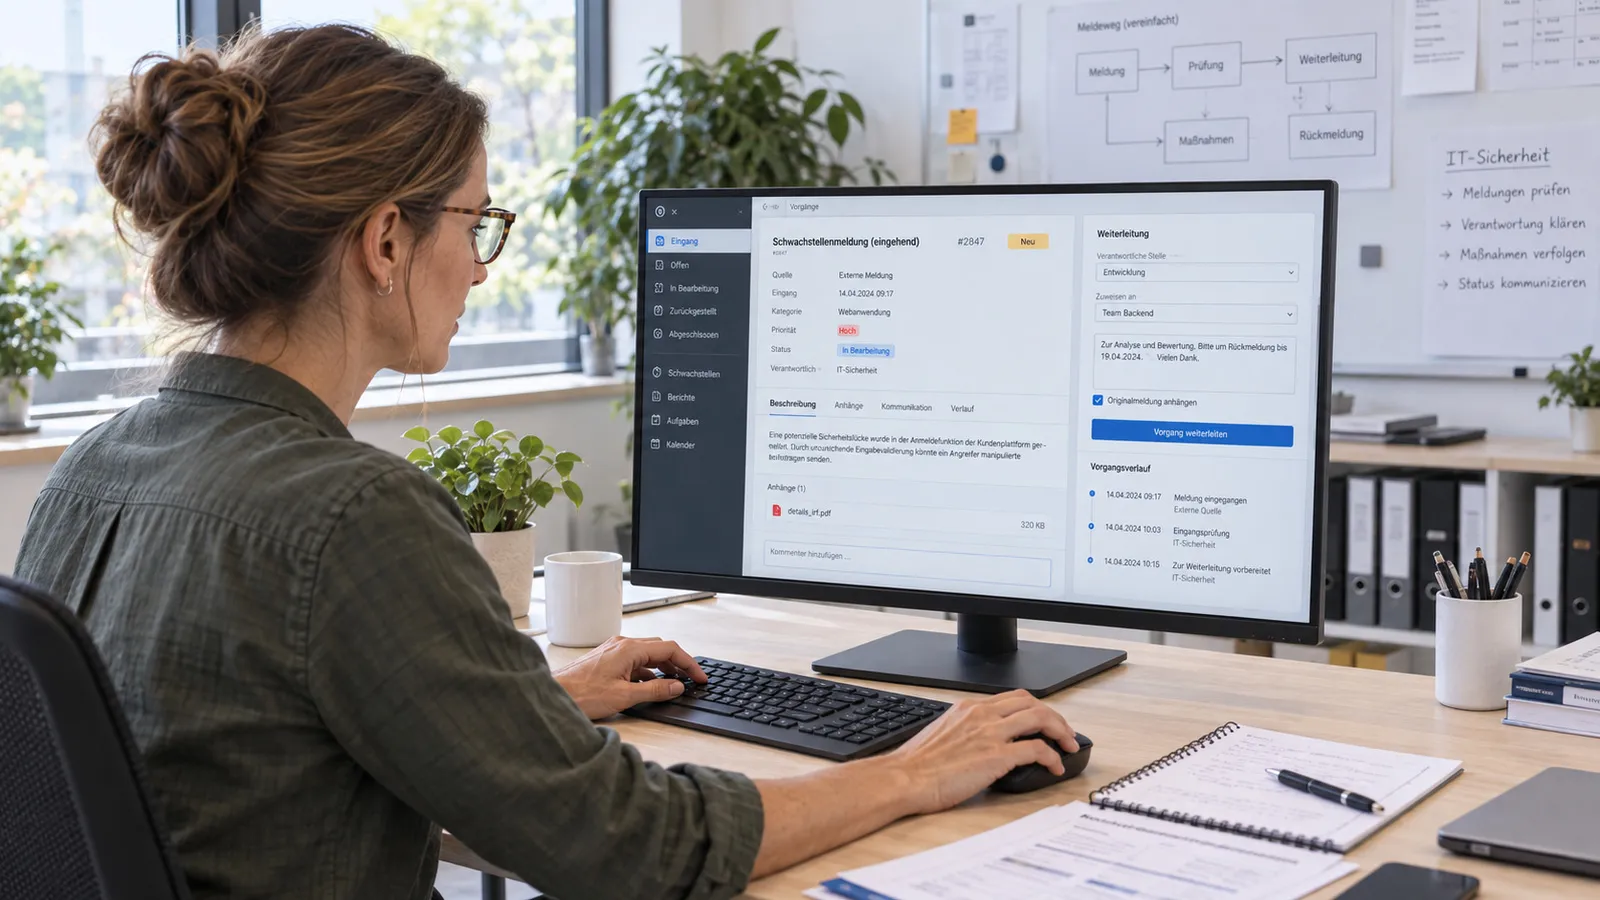
Monitor vulnerabilities
Manufacturer notices and CVE information are matched against the component inventory.
 Ai
4
Handle reporting channels
Incoming vulnerability reports are handled and forwarded in the ticket system.
The software stays within your own company.
The product goes to customers with modified components.
The software runs on the server side and is used over the network.
Scope boundary
Our documentation classifies components, licences and updates in a technically traceable way.
You clarify binding legal advice and final conformity decisions with your legal experts; our documents serve them as a basis.
We are glad to answer your detailed questions in a personal conversation.
The legal assessment lies with your legal advisers. IQstruct Engineering supplies the technical classification and documentation.
Whether and in which form an SBOM is required depends on the product and the applicable requirements. We take it into account as part of the component documentation.
Manufacturer notices are monitored; updates run via relevance assessment, testing, release, rollout and rollback.
Every industry has its particularities. That calls for a reliable partner who knows the requirements and delivers suitable solutions.
First conversation
Describe your task. We agree a date and discuss the possible project scope.
 Ai
1
You request an appointment
 Ai
2
We discuss your requirements
 Ai
3
You receive a quotation for the agreed scope
Describe your task in the contact form. We come back with a proposed date.
Arrange a first conversationBooking calendar
The booking calendar appears here. It loads only after your consent, because your browser connects to Microsoft in the process.
Discover further suitable services.
Combine automated tests, security checks and traceable releases.
Organise responsibilities, risks and evidence in an operable information security management system.
Prioritise findings and plan updates to suit your operating systems and plants.
