


Separate network areas by task
Production, office and connected services are assigned deliberately.
Suggestions appear from three characters.
No match. Try another term or choose a topic below.
Validate the controller against a model
The topic area at a glance
Customers we work for
Joint projects and their results
Working at IQstruct Engineering
ISO 9001 and TISAX
Alliances, associations, marketplaces
Quality policy and certificate
Separate production and office areas and define the communication paths required.
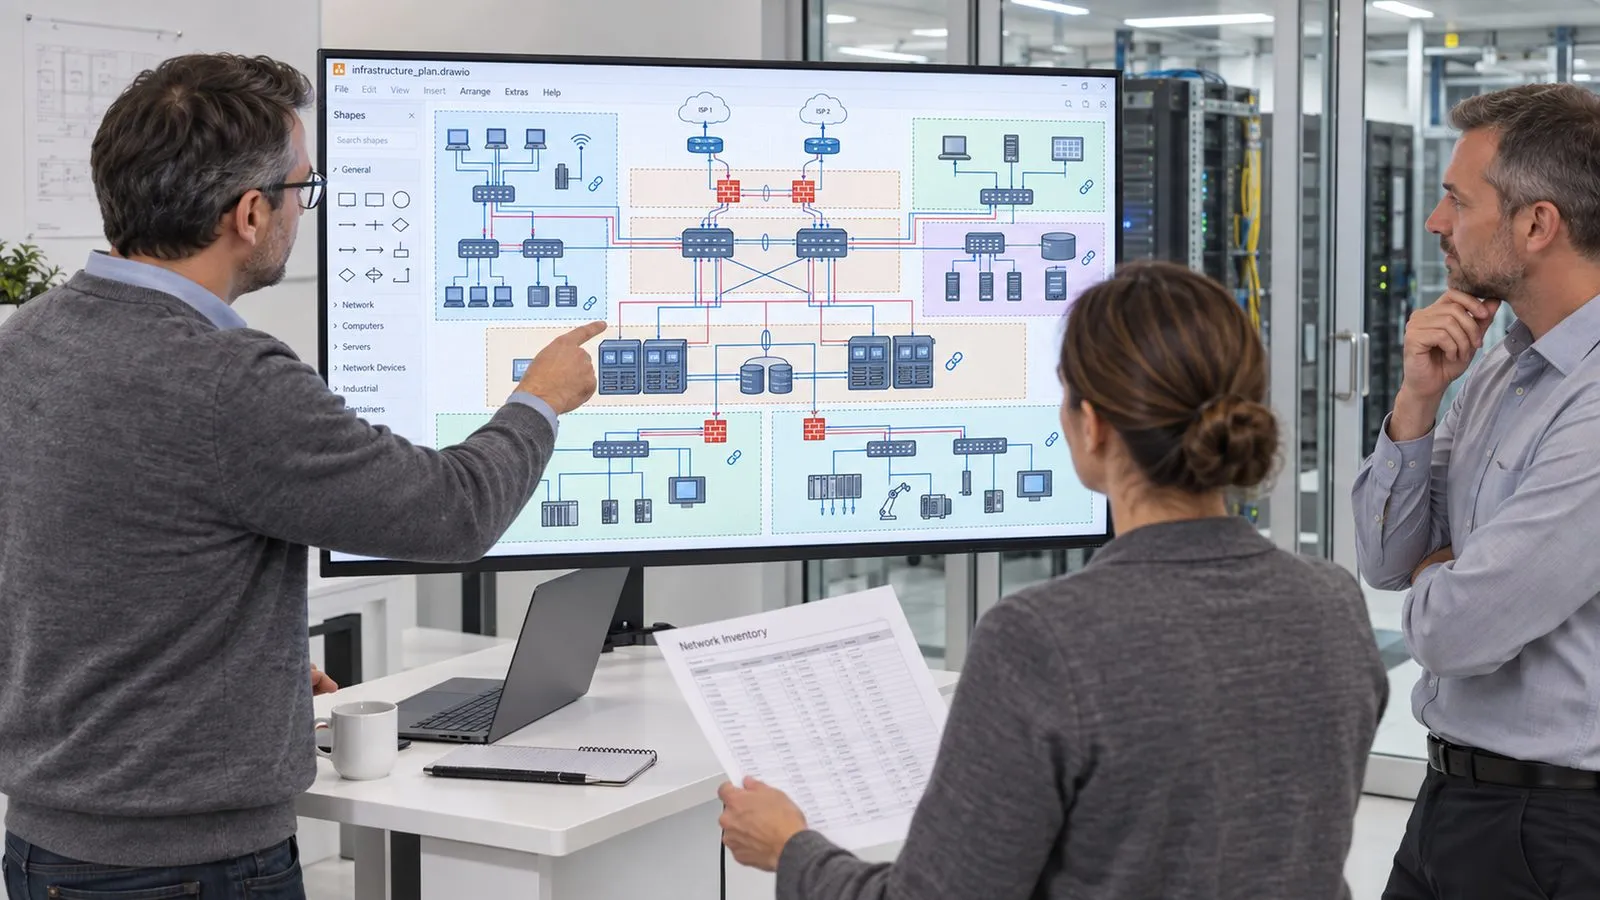
Flat networks make data access easy, but also hard to limit. With new IIoT and remote maintenance connections, it has to remain clear which systems may communicate with each other.
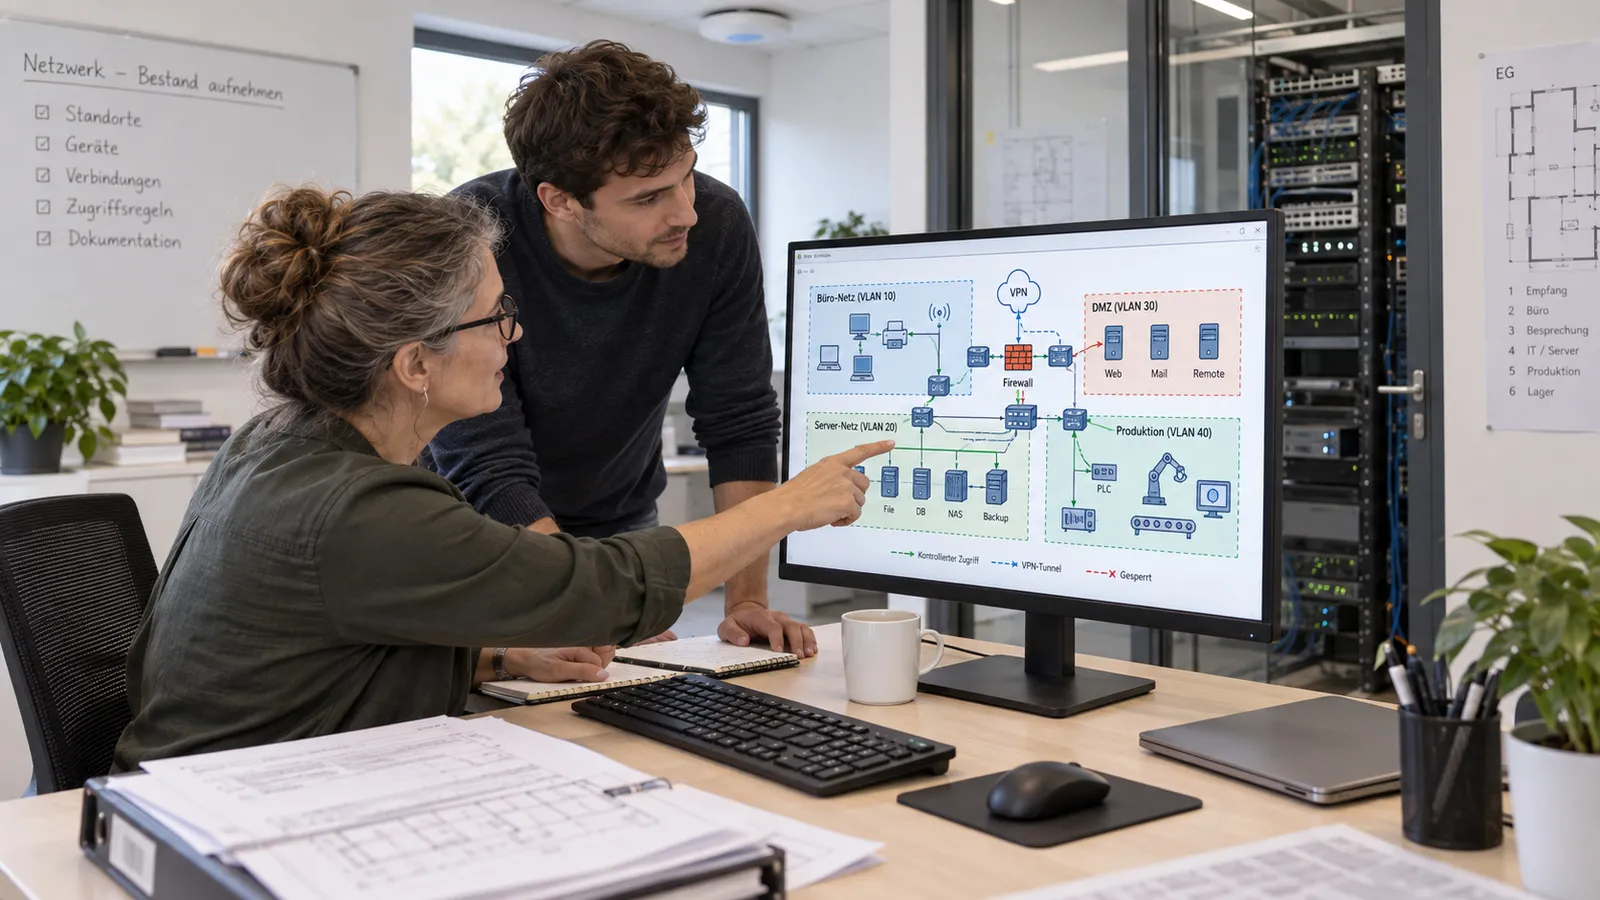
IQstruct Engineering develops segmentation and hardening concepts and implements controlled connections. VLANs, firewalls, DMZ structures and allowlisting are coordinated with applications and operation. Zones and their connections help to organise the architecture in a traceable way.
In a free first conversation we look at your network plan and name the first dividing line.
Production, office and connected services are assigned deliberately.
Communication is aligned with the exchange required.
Remote maintenance, backup and monitoring are integrated into the architecture.
IQstruct Engineering develops segmentation and hardening concepts and implements controlled connections.
After a survey, VLANs, firewalls, DMZ structures and allowlisting are coordinated with applications and operation. Zones and the connections between them organise the architecture in a traceable way.
A middleware between machine and IT opens up a new data path. Its ports and directions of communication are therefore included in the network concept, as are remote maintenance and backup. Data access thus remains limited to the systems that need it.
Network security
With new IIoT and remote maintenance connections, it remains clear which systems may communicate with each other.
 Ai
1
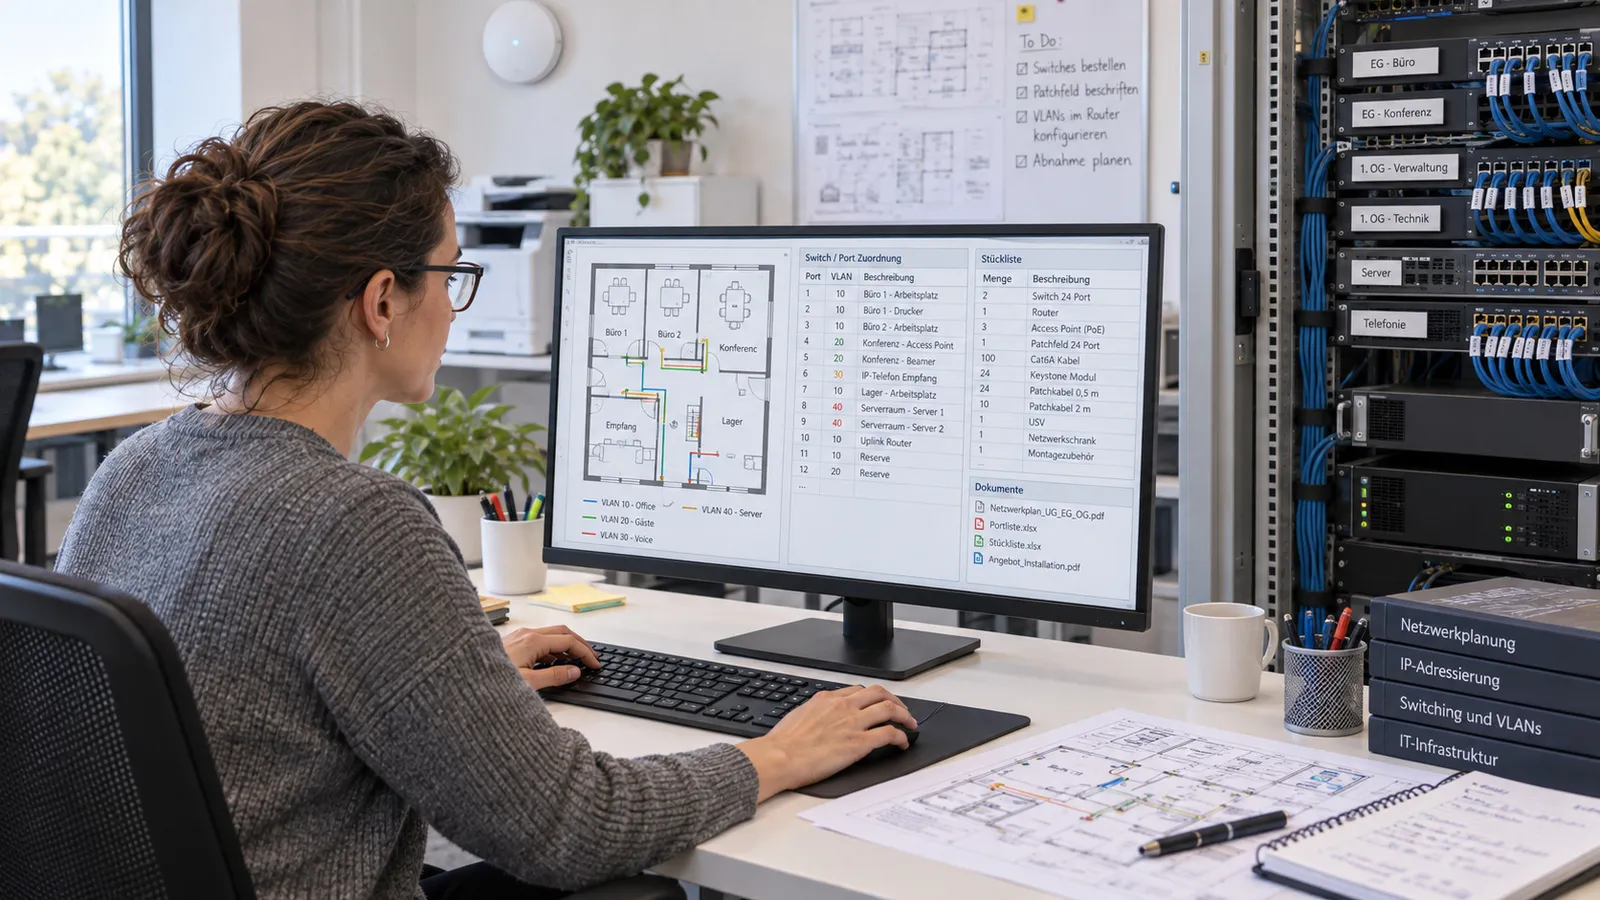
Record the network inventory
Office IT, production, servers, NAS and transitions are shown in one network diagram.
 Ai
2
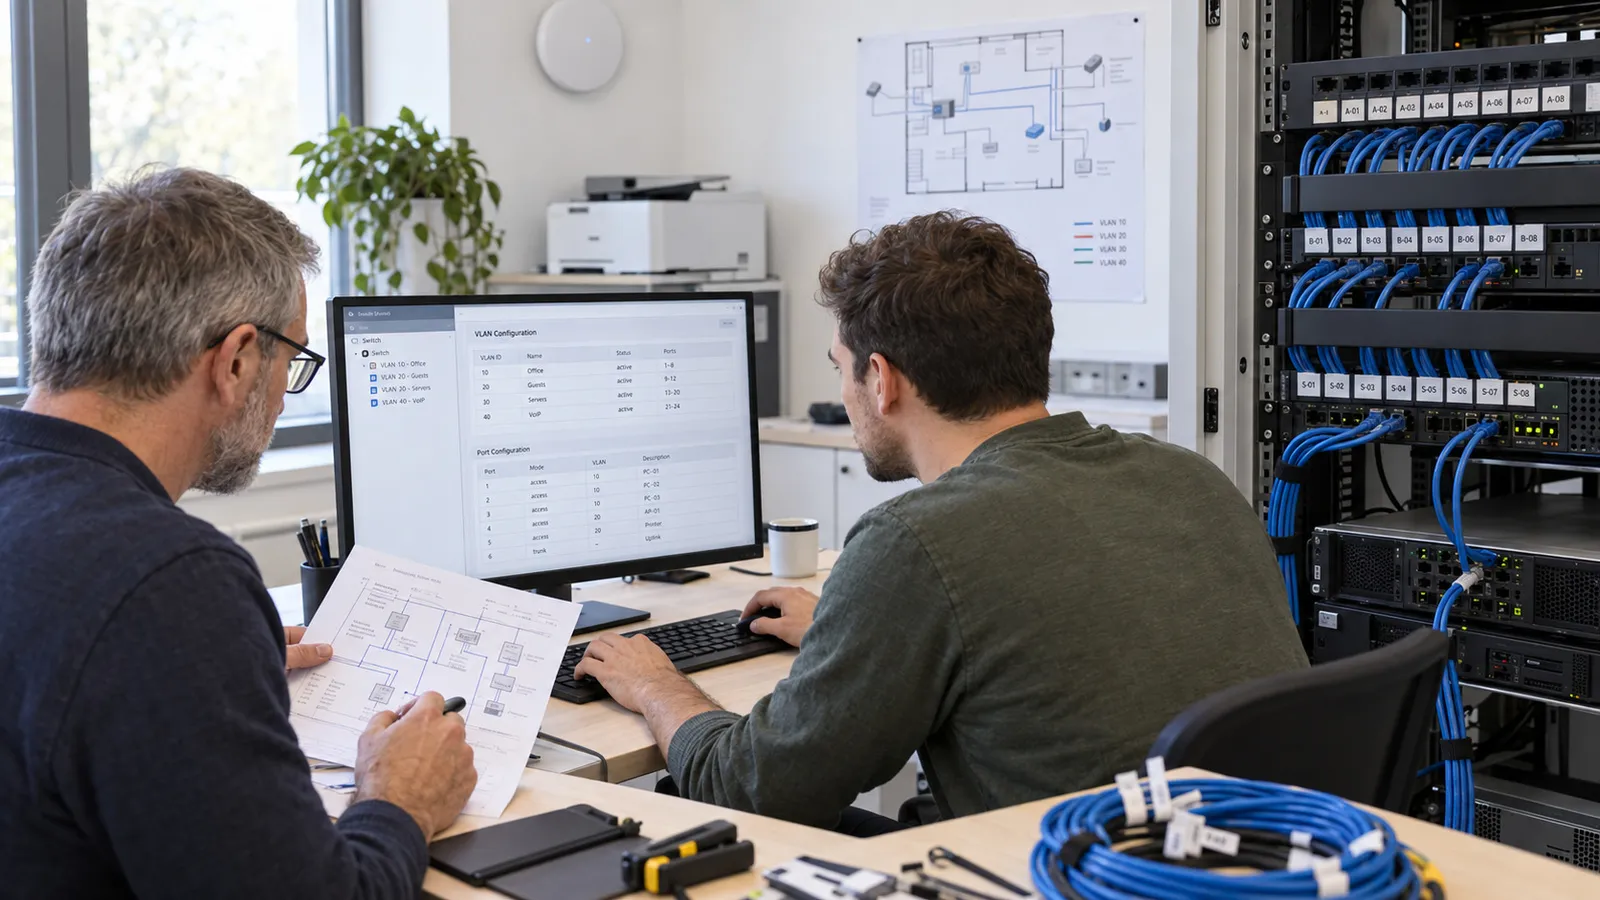
Design the network
Switches, routers, VLANs and patch panels are planned with labelled ports.
 Ai
3
Install the network
Cabling and devices are installed with labels, and the VLANs are configured.
 Ai
4
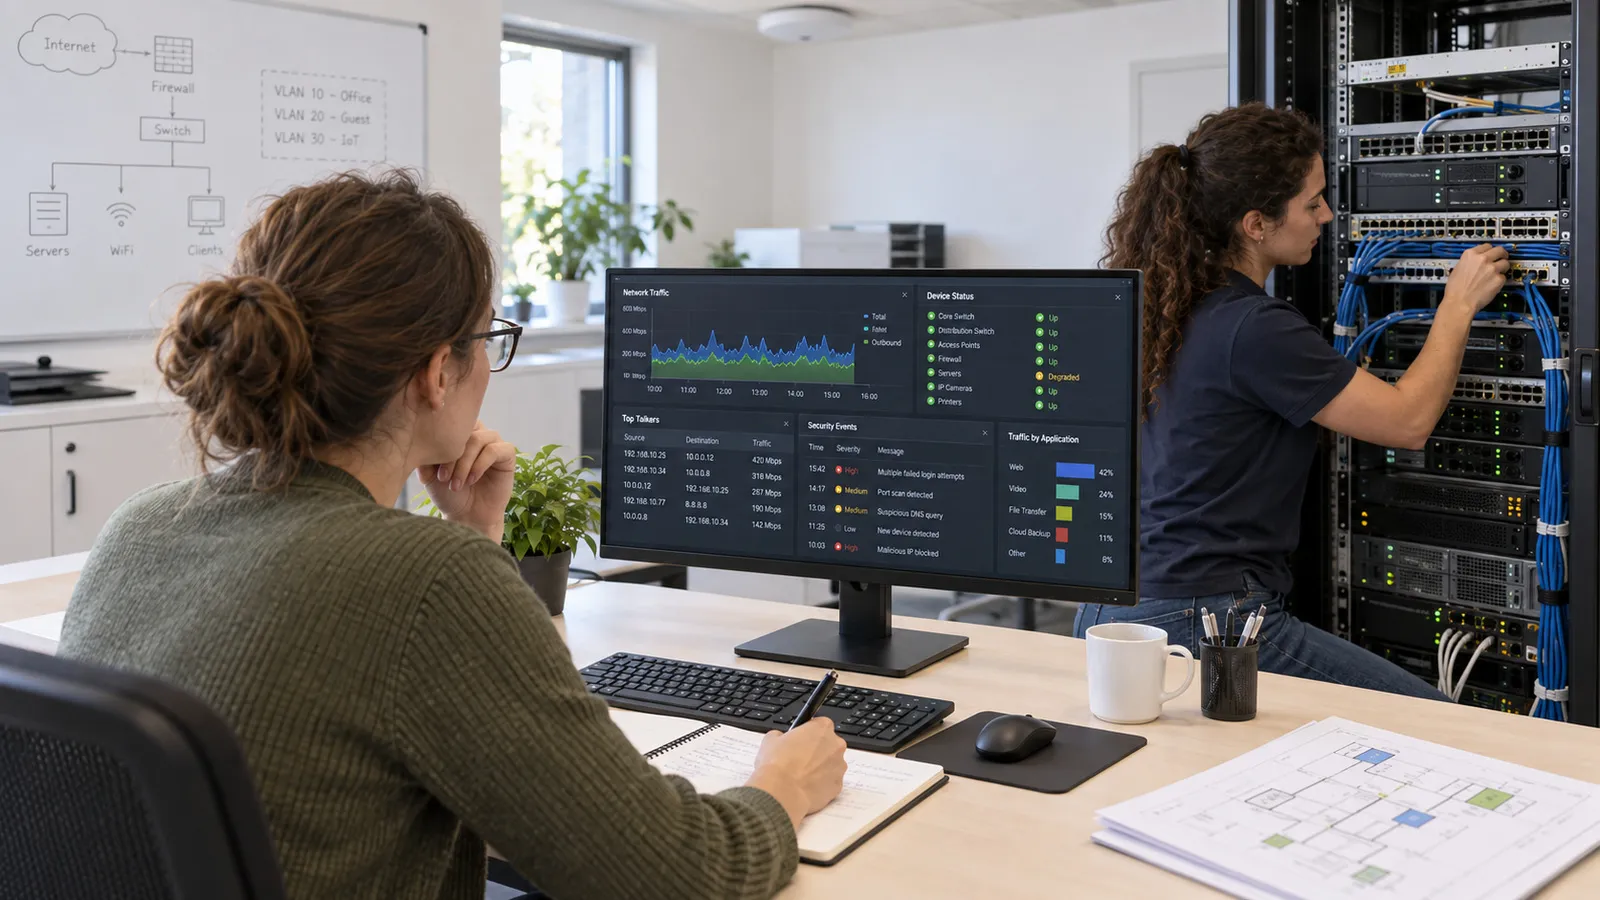
Monitor the network
Traffic, states and security findings are reviewed in monitoring.
Separate network areas for production, office and services.
Controlled transitions between the zones.
Only released communication between defined systems.
Information security
In the automotive industry, TISAX creates a common basis for handling confidential information.
Manufacturers and suppliers exchange design data, software and further sensitive project information. TISAX makes it possible to assess information security against common criteria and to share the results with business partners. As an engineering service provider in this supply chain, IQstruct Engineering likewise commits to protecting the information entrusted to it and holds a TISAX label. Clear access rights, governed data exchange and traceable responsibilities are therefore part of the cooperation in a project as well.
We are glad to answer your detailed questions in a personal conversation.
Network separation needs rules for communication and access. We coordinate these rules with the connections your systems need.
The ports and directions of communication of the middleware are included in the network concept and limited to the data exchange required.
Yes. Remote access is integrated into the segmentation.
Every industry has its particularities. That calls for a reliable partner who knows the requirements and delivers suitable solutions.
First conversation
Describe your task. We agree a date and discuss the possible project scope.
 Ai
1
You request an appointment
 Ai
2
We discuss your requirements
 Ai
3
You receive a quotation for the agreed scope
Describe your task in the contact form. We come back with a proposed date.
Arrange a first conversationBooking calendar
The booking calendar appears here. It loads only after your consent, because your browser connects to Microsoft in the process.
Discover further suitable services.
Connect office, server and machine networks with a coordinated switching and routing structure.
Connect machine knowledge with segmentation, access protection and planned operation.
Limit external access to released systems, people and time windows.
