


Release target systems specifically
Access is aligned with the agreed need.
Suggestions appear from three characters.
No match. Try another term or choose a topic below.
Validate the controller against a model
The topic area at a glance
Customers we work for
Joint projects and their results
Working at IQstruct Engineering
ISO 9001 and TISAX
Alliances, associations, marketplaces
Quality policy and certificate
Limit external access to released systems, people and time windows.
Service partners need access without entire network areas becoming permanently reachable as a result. Remote access has to fit segmentation and operating responsibility.
IQstruct Engineering plans and integrates remote access with suitable access paths. VPN, jump hosts, MFA and time-limited releases can be combined. The choice is coordinated with the existing infrastructure, roles and security requirements.
In a free first conversation we clarify which suppliers have access today and what the controlled way there looks like.
Access is aligned with the agreed need.
Multi-factor sign-in and time-limited authorisation complement the technical access.
Responsibilities and agreed service hours determine the procedure.
IQstruct Engineering plans and integrates secure remote access for machines and industrial systems.
VPN, jump hosts, multi-factor authentication and time-limited releases are combined and adapted to the infrastructure, the role model and the security requirements.
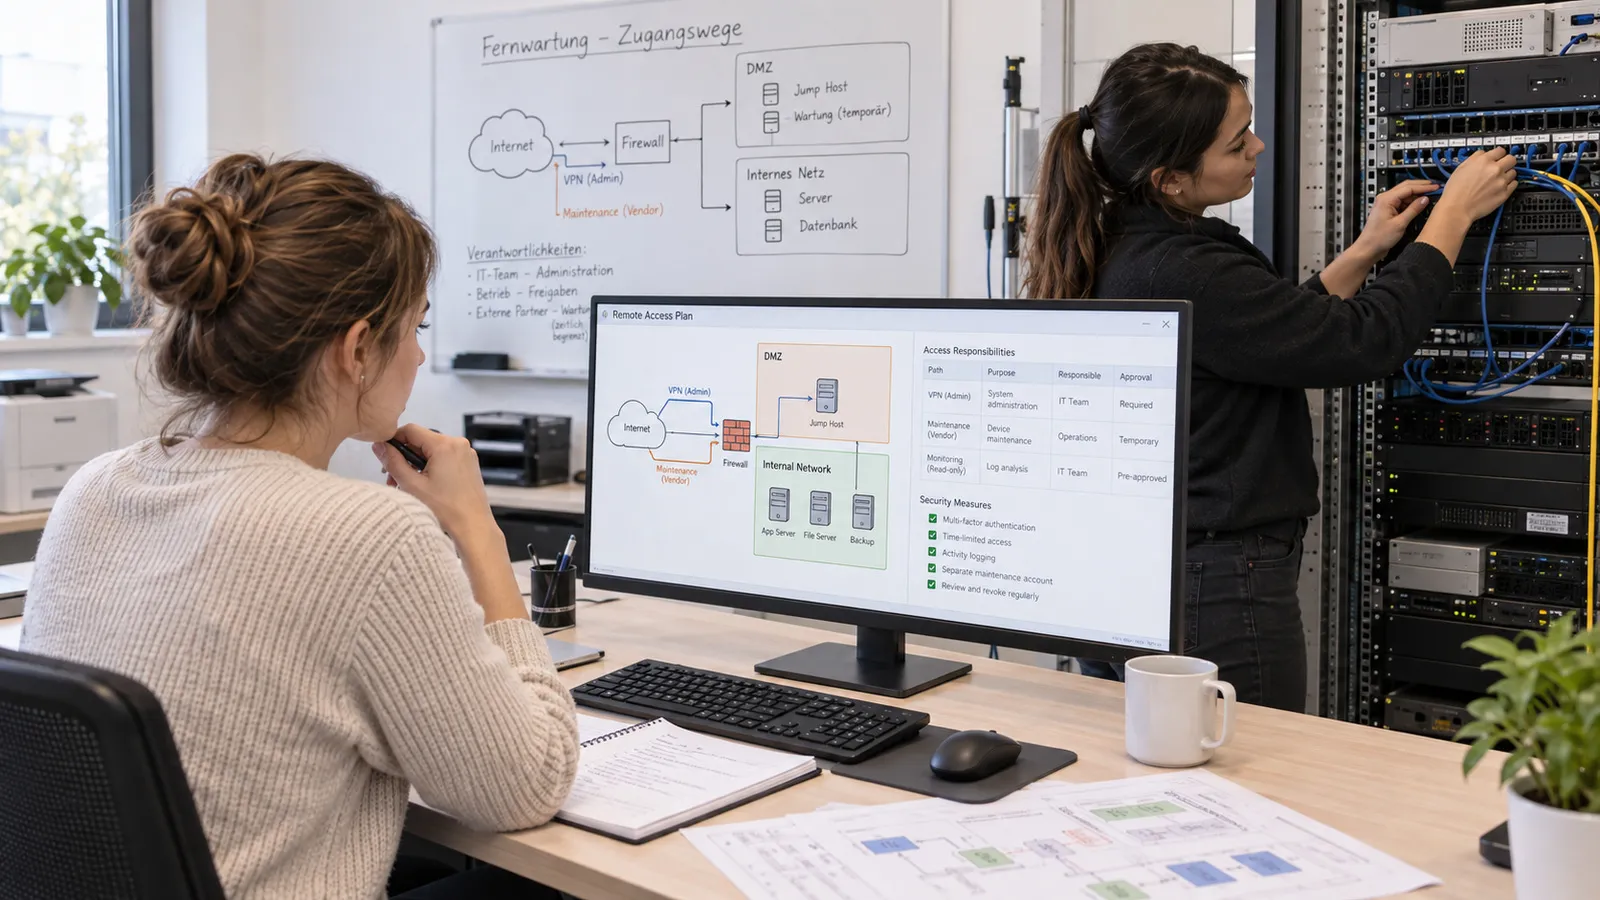
External access is set up for a specific occasion. Target system, authorised person and release period are therefore part of the planning. The connection with identity services and network segmentation embeds remote access in operating responsibility; support hours and responsibility are set out in the scope of service.
Remote access
Access applies to defined systems, people and time windows, and entire network areas stay closed.
 Ai
1
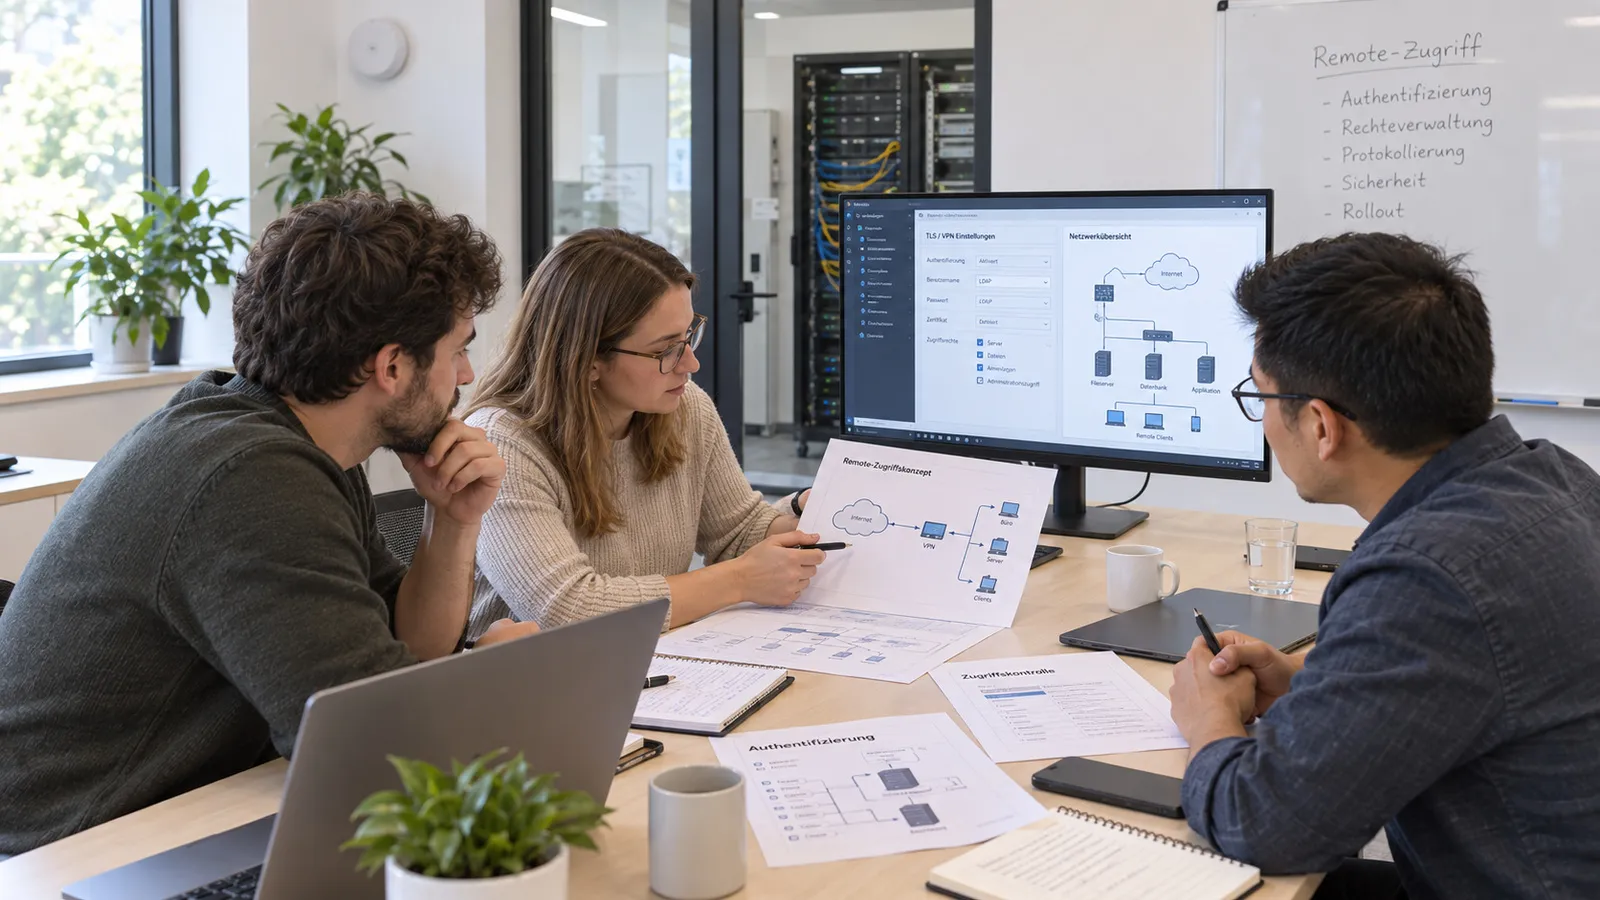
Plan remote access
Incoming and outgoing maintenance paths are defined with responsibilities.
 Ai
2
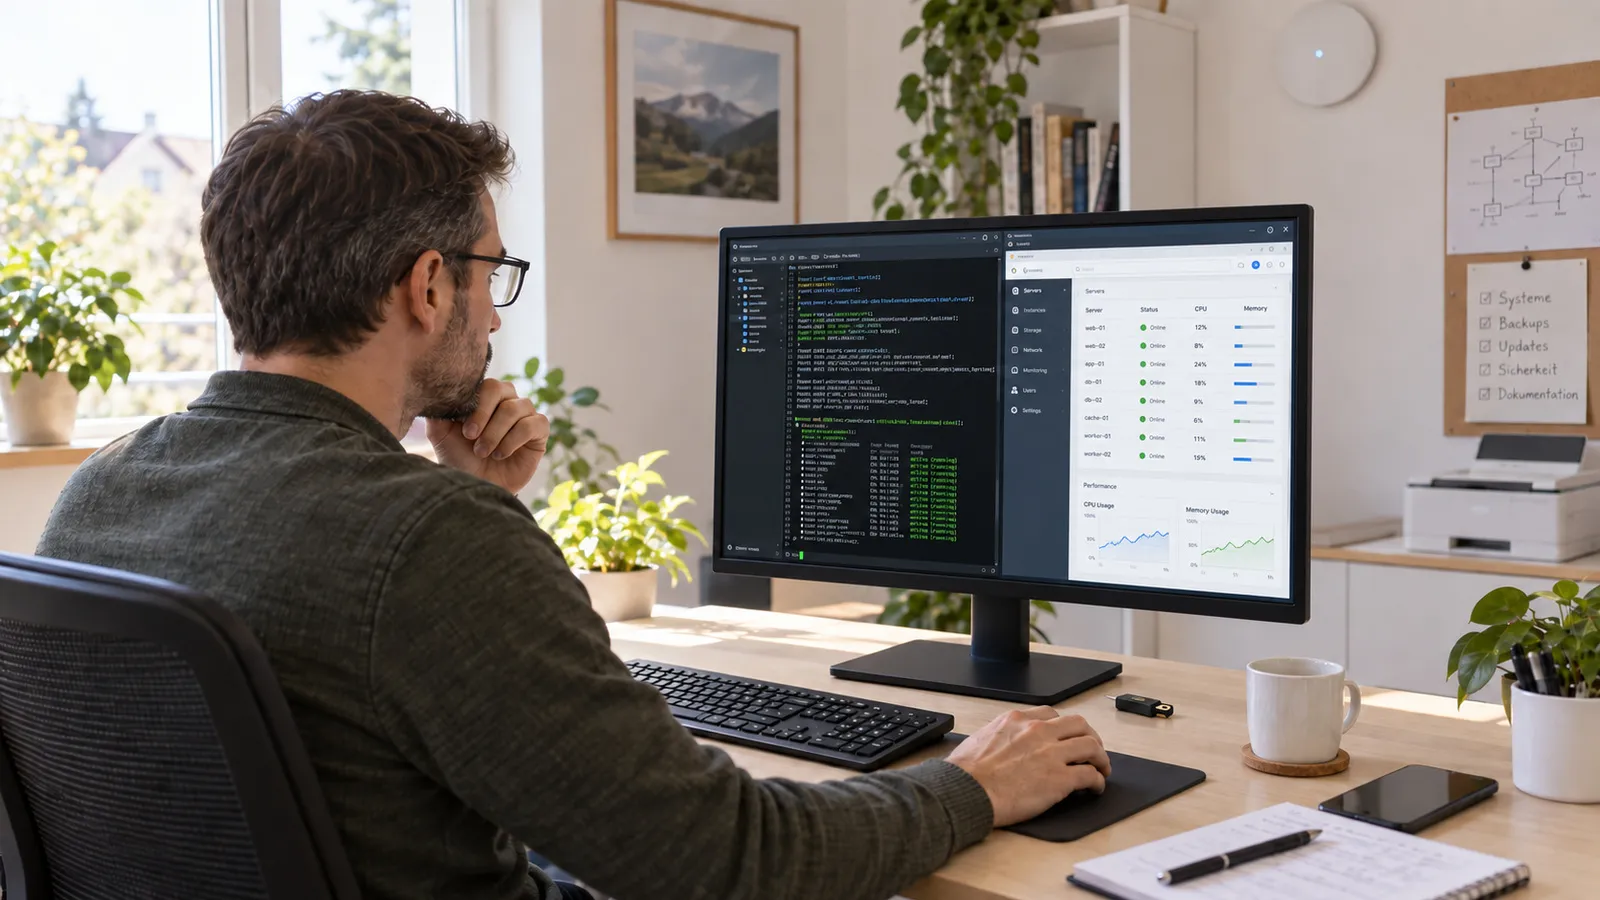
Set up remote access
Access on computers and servers is configured with authentication.
 Ai
3
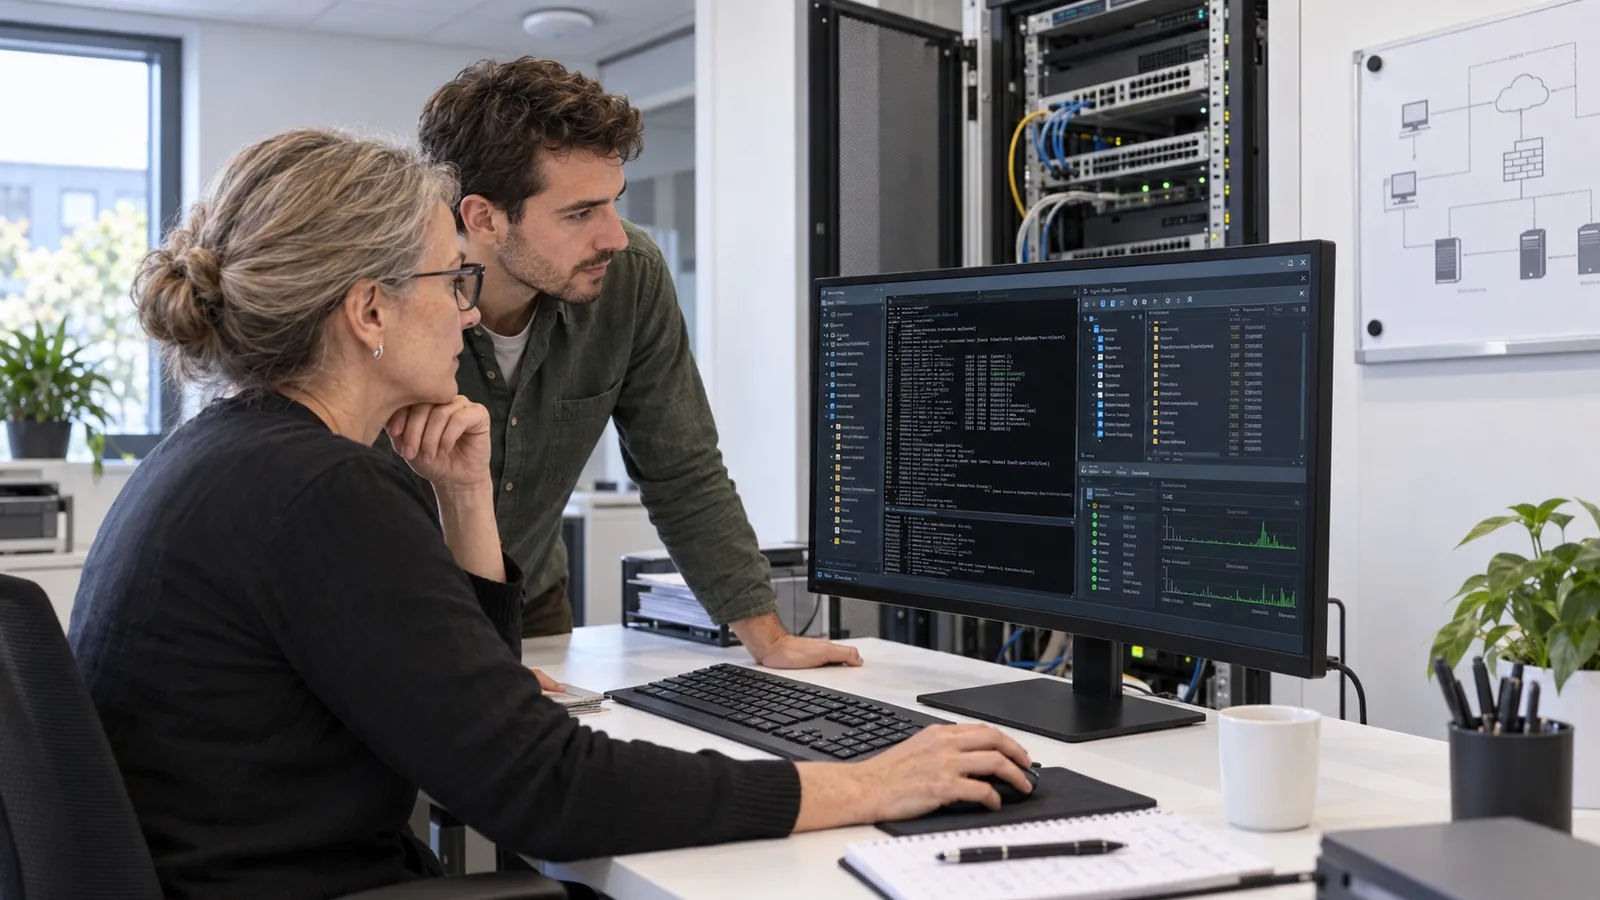
Use access into the company
Authorised specialists maintain company systems via the released access.
 Ai
4
Maintain customer systems remotely
Employees access customer systems under control and for a limited time.
Encrypted connection into the released network area.
A controlled intermediate point in front of the target system.
Access only applies for the agreed period.
IT/OT
Changes to servers and access often affect several systems at once.
A certified IT security auditor (TÜV) works in the team. The access paths are chosen vendor-neutrally to match your infrastructure. Dependencies, access paths and affected applications are therefore reviewed together before a change. The agreed procedure includes a maintenance window, the functional test and a documented way back. Ongoing support keeps configurations and responsibilities current, so that later extensions stay traceable as well.
We are glad to answer your detailed questions in a personal conversation.
We coordinate access rights, releases and service hours with your operation.
The choice is made per project to suit your infrastructure and your security requirements.
We define service hours and response targets in the scope of service.
Every industry has its particularities. That calls for a reliable partner who knows the requirements and delivers suitable solutions.
First conversation
Describe your task. We agree a date and discuss the possible project scope.
 Ai
1
You request an appointment
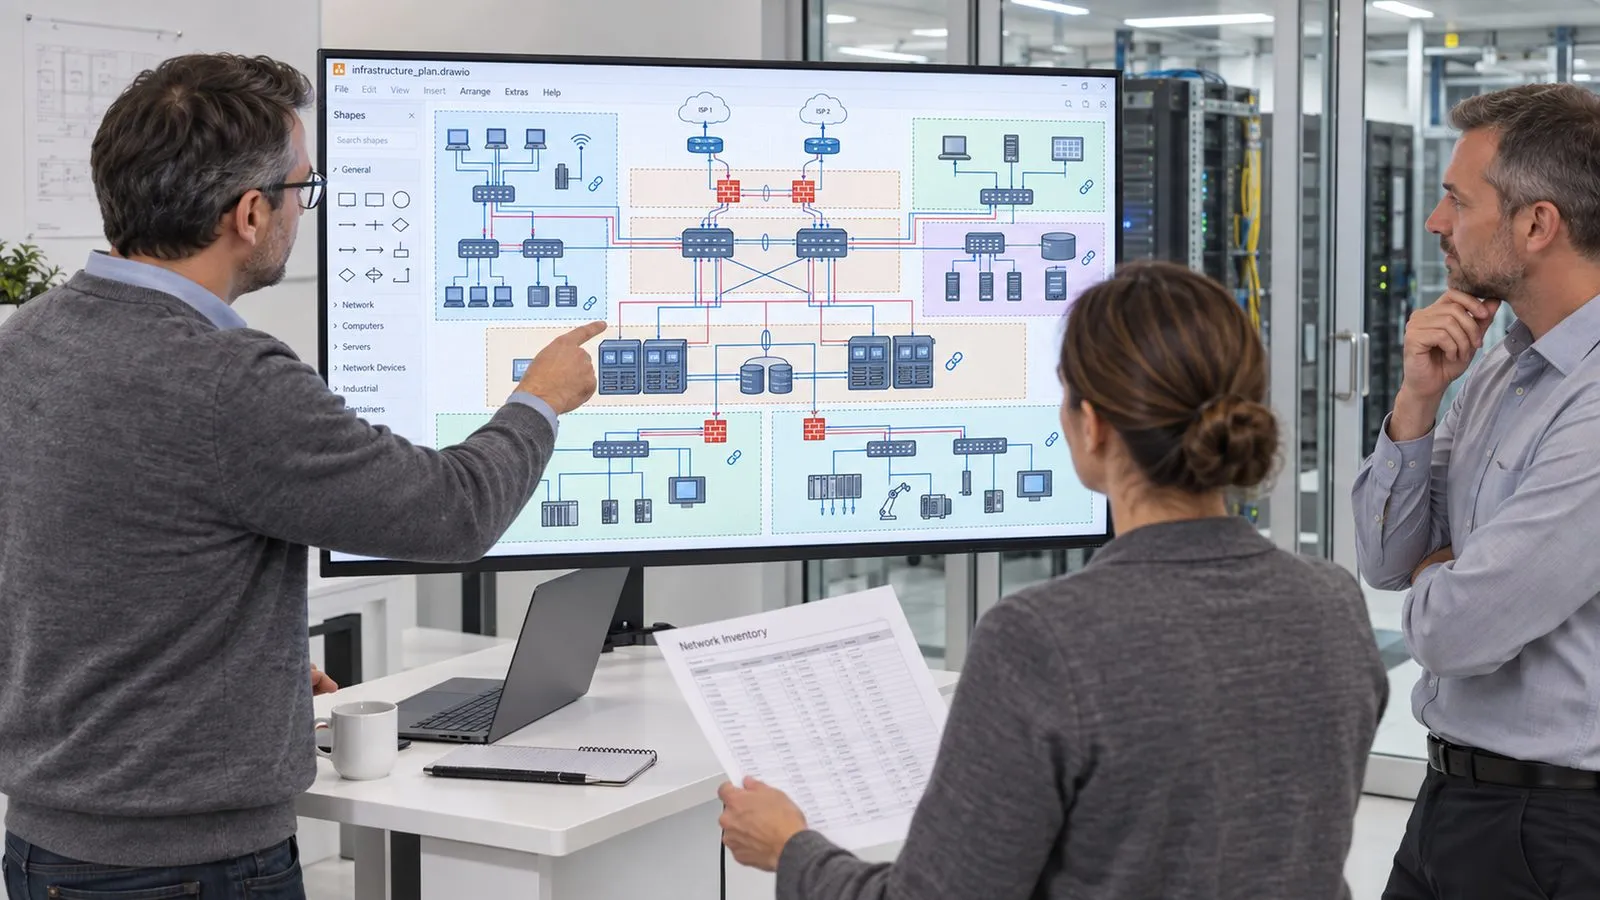 Ai
2
We discuss your requirements
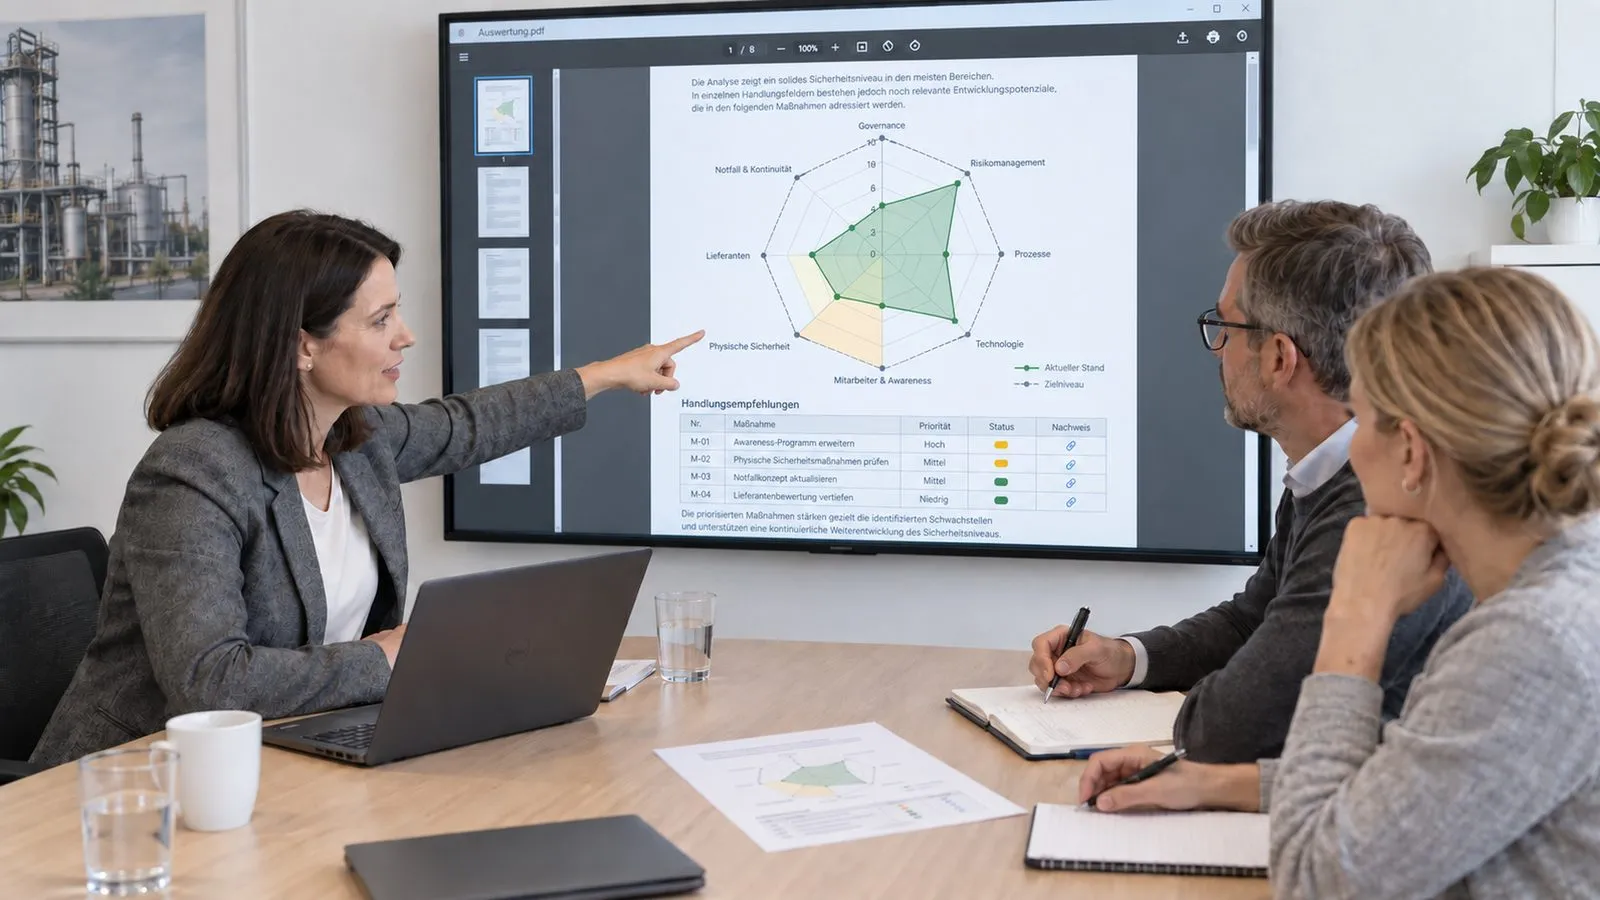 Ai
3
You receive a quotation for the agreed scope
Describe your task in the contact form. We come back with a proposed date.
Arrange a first conversationBooking calendar
The booking calendar appears here. It loads only after your consent, because your browser connects to Microsoft in the process.
Discover further suitable services.
Separate production and office areas and define the communication paths required.
Connect applications with central identities, roles and multi-factor authentication.
Combine monitoring, updates and support in one agreed operating model.
